Buy xxxnx.eu ?
We are moving the project
xxxnx.eu .
Are you interested in purchasing the domain
xxxnx.eu ?
domain@kv-gmbh.de · 0541-91531010
Buy xxxnx.eu ?
What is BitLocker TPM?
BitLocker TPM (Trusted Platform Module) is a security feature in Windows operating systems that uses a hardware component called TPM to provide enhanced protection for data stored on a computer's hard drive. TPM is a microchip that securely stores encryption keys, passwords, and other sensitive information to help protect against unauthorized access to the system. When BitLocker TPM is enabled, the encryption keys are securely stored in the TPM, making it more difficult for attackers to access the data even if they physically remove the hard drive from the computer. **
Can't you activate TPM?
Yes, TPM (Trusted Platform Module) can be activated on compatible devices through the device's BIOS settings. However, not all devices have TPM built-in, so it's important to check the device's specifications to see if TPM is available. Once activated, TPM provides hardware-based security features such as secure boot, device encryption, and key management to help protect sensitive data and ensure the integrity of the system. **


Similar search terms for Tpm
Top-Angebote
Products related to Tpm:
-
Montale Sensual Instinct EDP U 50 mlMontale Sensual Instinct, 50 ml, Eaux de Parfum unisex, New day – new opportunity to tackle more challenges. Montale Sensual Instinct unisex Eau de Parfum will refresh your mind so that you can boldly follow your instinct. Embrace your everyday adventures! unique fragrance for a unique personality unisex – suitable for both women and men74,00 £*Shipping: 3,99 £Secure redirect to the provider
-
Oriflame Love Potion Sensual Ruby EDP W 50 mlOriflame Love Potion Sensual Ruby, 50 ml, Eaux de Parfum for Women, Treat your senses to a true gourmand experience. Oriflame Love Potion Sensual Ruby Eau de Parfum for women offers delicious notes that are nearly impossible to resist – especially if you love your sweets. gourmand fragrance floral fragrance brings out the sensuality in every woman suitable for everyday wear luxury fragrance for connoisseurs19,80 £*Shipping: 3,99 £Secure redirect to the provider


-
What exactly is TPM 2.0?
TPM 2.0, which stands for Trusted Platform Module 2.0, is a hardware-based security feature that provides a secure foundation for various security functions, such as encryption, authentication, and key management. It is a microcontroller that is typically integrated into computer systems to enhance security by securely storing sensitive information, such as encryption keys, digital certificates, and passwords. TPM 2.0 helps protect against various security threats, including unauthorized access, malware attacks, and data breaches, by providing a secure environment for sensitive data and cryptographic operations. **
-
How do I activate TPM?
To activate TPM (Trusted Platform Module) on your computer, you will need to access the BIOS or UEFI settings. Restart your computer and enter the BIOS/UEFI by pressing a specific key (usually F2, F10, or Del) during the boot-up process. Look for the TPM settings in the security or advanced settings section and enable TPM. Save the changes and exit the BIOS/UEFI settings. TPM should now be activated on your computer. **
-
How can one delete TPM?
To delete TPM (Trusted Platform Module) on a computer, you would need to access the computer's BIOS or UEFI settings. Once in the settings, you can navigate to the security or TPM section and find the option to clear or reset the TPM. This will remove any existing TPM data and settings from the computer. It's important to note that deleting TPM may have implications for the computer's security and functionality, so it should only be done if necessary and with caution. **
-
Does it support TPM 2.0?
Yes, the device supports TPM 2.0. TPM (Trusted Platform Module) 2.0 is a security feature that provides hardware-based security functions, such as cryptographic keys and secure boot, to help protect the device from unauthorized access and tampering. This ensures that the device has a secure foundation for running trusted applications and protecting sensitive data. **
How can I update TPM?
To update TPM (Trusted Platform Module), you can follow these steps: 1. Check for TPM firmware updates on the manufacturer's website or through the device's management software. 2. Download the latest TPM firmware update and follow the instructions provided by the manufacturer for installation. 3. Ensure that your device is connected to a stable power source and that all other applications are closed during the update process. 4. Restart your device after the update is complete to ensure that the changes take effect. It's important to regularly check for TPM updates to ensure that your device has the latest security features and bug fixes. **
Which one fits with TPM 20?
TPM 2.0 (Trusted Platform Module 2.0) is a hardware-based security solution that is designed to provide a secure foundation for various computing devices. It is typically integrated into the motherboard of a device and provides features such as secure boot, cryptographic key generation and storage, and hardware-based device authentication. TPM 2.0 is designed to enhance the security of devices and protect against various types of attacks, making it a suitable choice for organizations and individuals looking to secure their computing infrastructure. **
Top-Angebote
Products related to Tpm:
-
Asus TPM-SPI V2.0 Security TPM ModuleThe ASUS TPM SPI V2.0 Security Module is designed to enhance computer security by providing dedicated hardware based protection for compatible systems. It helps securely store encryption keys, digital certificates, passwords and other sensitive information. Using a 14-1 pin SPI interface, the module is designed for compatible ASUS motherboards and systems that support the TPM SPI standard. It provides a dedicated Trusted Platform Module solution for systems requiring hardware based security features. The module uses the Nuvoton NPCT750 security chip and complies with the Trusted Computing Group TPM 2.0 specification. This allows it to support security functions that help protect platform integrity and digital identities. Security certifications include Common Criteria EAL4+ and FIPS 140-2. The module also meets CE and RoHS compliance requirements, providing a certified solution for compatible computing platforms. The ASUS TPM SPI V2.0 is a compact internal security accessory designed for straightforward motherboard integration. Before installation, compatibility should be checked carefully because TPM SPI and TPM LPC modules use different pin definitions and are not interchangeable.15,99 £*Shipping: 0,00 £Secure redirect to the provider
-
Montale Sensual Instinct EDP U 50 mlMontale Sensual Instinct, 50 ml, Eaux de Parfum unisex, New day – new opportunity to tackle more challenges. Montale Sensual Instinct unisex Eau de Parfum will refresh your mind so that you can boldly follow your instinct. Embrace your everyday adventures! unique fragrance for a unique personality unisex – suitable for both women and men74,00 £*Shipping: 3,99 £Secure redirect to the provider
-
What is BitLocker TPM?
BitLocker TPM (Trusted Platform Module) is a security feature in Windows operating systems that uses a hardware component called TPM to provide enhanced protection for data stored on a computer's hard drive. TPM is a microchip that securely stores encryption keys, passwords, and other sensitive information to help protect against unauthorized access to the system. When BitLocker TPM is enabled, the encryption keys are securely stored in the TPM, making it more difficult for attackers to access the data even if they physically remove the hard drive from the computer. **
-
Can't you activate TPM?
Yes, TPM (Trusted Platform Module) can be activated on compatible devices through the device's BIOS settings. However, not all devices have TPM built-in, so it's important to check the device's specifications to see if TPM is available. Once activated, TPM provides hardware-based security features such as secure boot, device encryption, and key management to help protect sensitive data and ensure the integrity of the system. **
-
What exactly is TPM 2.0?
TPM 2.0, which stands for Trusted Platform Module 2.0, is a hardware-based security feature that provides a secure foundation for various security functions, such as encryption, authentication, and key management. It is a microcontroller that is typically integrated into computer systems to enhance security by securely storing sensitive information, such as encryption keys, digital certificates, and passwords. TPM 2.0 helps protect against various security threats, including unauthorized access, malware attacks, and data breaches, by providing a secure environment for sensitive data and cryptographic operations. **
-
How do I activate TPM?
To activate TPM (Trusted Platform Module) on your computer, you will need to access the BIOS or UEFI settings. Restart your computer and enter the BIOS/UEFI by pressing a specific key (usually F2, F10, or Del) during the boot-up process. Look for the TPM settings in the security or advanced settings section and enable TPM. Save the changes and exit the BIOS/UEFI settings. TPM should now be activated on your computer. **
Similar search terms for Tpm
-
Oriflame Love Potion Sensual Ruby EDP W 50 mlOriflame Love Potion Sensual Ruby, 50 ml, Eaux de Parfum for Women, Treat your senses to a true gourmand experience. Oriflame Love Potion Sensual Ruby Eau de Parfum for women offers delicious notes that are nearly impossible to resist – especially if you love your sweets. gourmand fragrance floral fragrance brings out the sensuality in every woman suitable for everyday wear luxury fragrance for connoisseurs19,80 £*Shipping: 3,99 £Secure redirect to the provider
-
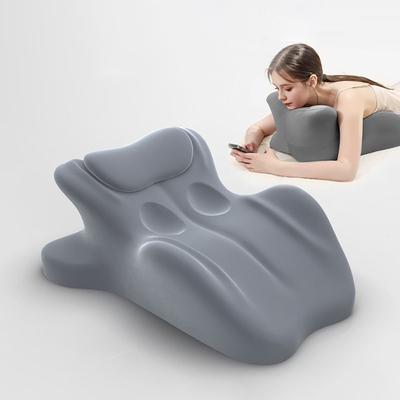
Youfap Market Memory Foam Wedge, Couple Pillow For Intimacy & Support, Lumbar Neck Support Memory Foam Wedge, Couple Pillow For Intimacy & Support, Lumbar Neck SupportUltimate Comfort and Support for Intimacy Designed for couples seeking better comfort, the Couple Pillow for Intimacy & Support features a memory foam wedge that helps achieve the perfect position during intimate moments. Its unique shape promotes...99,97 $*Shipping: 0,00 $Secure redirect to the provider
-
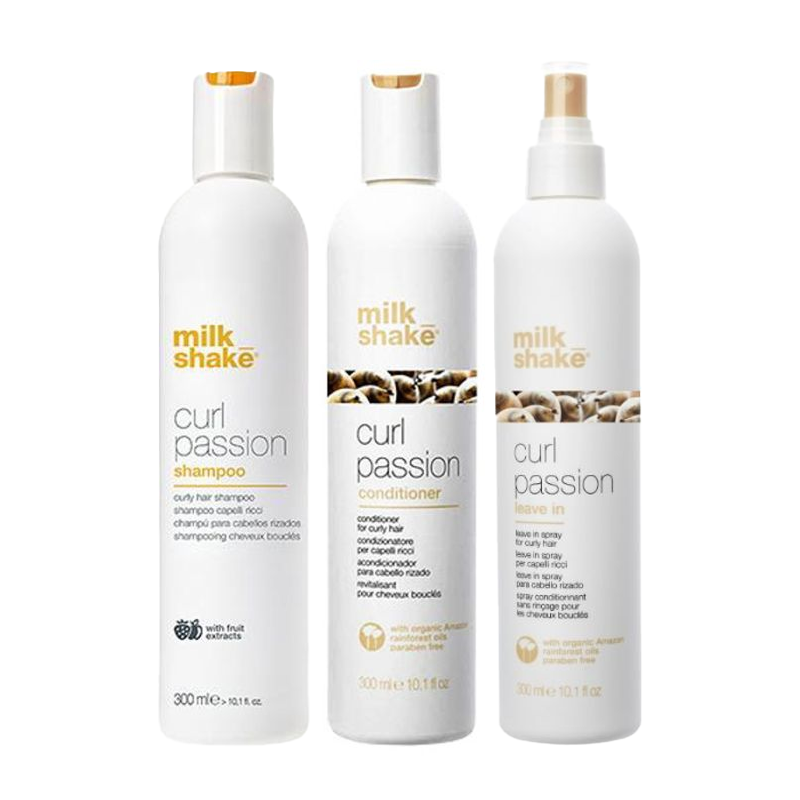
milk_shake curl passion shampoo 300ml, curl passion conditioner 300mlGently cleanse your hair while caring for your curls with this curly cleansing and conditioning pack from milk_shake. With professional-standard oils and natural ingredients, the Curl Passion Shampoo by milk_shake reinforces your hair's natural shape and eliminates frizz so it looks and feels stronger and healthier than ever. Enriched with organic milk and quinoa proteins as well as fruit extracts and organic pracaxi and babassu oils, the milk_shake Curl Passion Conditioner boosts softness and manageability, without weighing the hair down. The brand new milk_shake Leave In Conditioning Treatment is a treatment spray to help make curls soft, bouncy, flexible and long-lasting. Ingredients Leave In: Aqua (Water), PEG-40 Hydrogenated Castor Oil, Amodimethicone, Cetrimonium Chloride, Polyester-37, Polyquaternium-22, Hydrolyzed Milk Protein, Trideceth-12, Hydrolyzed Quinoa, Helianthus Annuus (Sunflower) Seed Extract, Citrus Limon (Lemon) Fruit Extract, Vaccinium Myrtillus Fruit Extract, Pyrus Malus (Apple) Fruit Extract, Orbignya Oleifera Seed Oil, Pentaclethra Macroloba Seed Oil, Parfum (Fragrance), Phenoxyethanol, Caprylyl Glycol, Citric Acid, Butylene Glycol, Benzyl Alcohol, Tocopherol, Amyl Cinnamal, Benzyl Benzoate, Benzyl Salicylate, Citronellol, Coumarin, Geraniol, Hexyl Cinnamal, Limonene, Linalool.60,17 £*Shipping: 0,00 £Secure redirect to the provider
-
How can one delete TPM?
To delete TPM (Trusted Platform Module) on a computer, you would need to access the computer's BIOS or UEFI settings. Once in the settings, you can navigate to the security or TPM section and find the option to clear or reset the TPM. This will remove any existing TPM data and settings from the computer. It's important to note that deleting TPM may have implications for the computer's security and functionality, so it should only be done if necessary and with caution. **
-
Does it support TPM 2.0?
Yes, the device supports TPM 2.0. TPM (Trusted Platform Module) 2.0 is a security feature that provides hardware-based security functions, such as cryptographic keys and secure boot, to help protect the device from unauthorized access and tampering. This ensures that the device has a secure foundation for running trusted applications and protecting sensitive data. **
-
How can I update TPM?
To update TPM (Trusted Platform Module), you can follow these steps: 1. Check for TPM firmware updates on the manufacturer's website or through the device's management software. 2. Download the latest TPM firmware update and follow the instructions provided by the manufacturer for installation. 3. Ensure that your device is connected to a stable power source and that all other applications are closed during the update process. 4. Restart your device after the update is complete to ensure that the changes take effect. It's important to regularly check for TPM updates to ensure that your device has the latest security features and bug fixes. **
-
Which one fits with TPM 20?
TPM 2.0 (Trusted Platform Module 2.0) is a hardware-based security solution that is designed to provide a secure foundation for various computing devices. It is typically integrated into the motherboard of a device and provides features such as secure boot, cryptographic key generation and storage, and hardware-based device authentication. TPM 2.0 is designed to enhance the security of devices and protect against various types of attacks, making it a suitable choice for organizations and individuals looking to secure their computing infrastructure. **
* All prices are inclusive of VAT and, if applicable, plus shipping costs. The offer information is based on the details provided by the respective shop and is updated through automated processes. Real-time updates do not occur, so deviations can occur in individual cases. ** Note: Parts of this content were created by AI.